
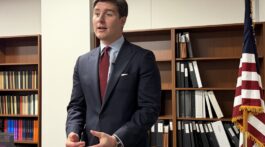

Indiana State Treasurer Daniel Elliott says aging technology, reliance on outside vendors and limited technical understanding among policymakers are contributing to cybersecurity risks for governments and businesses.
In an interview with Indy Politics, Elliott said recent cyber incidents reflect multiple problems rather than one isolated event. Some involve breaches at outside vendors, while others expose the challenges of connecting newer tools to older systems.
A group called None claimed it had obtained personal information belonging to JPMorgan Chase customers, Elliott said. He emphasized that the reported breach occurred at a vendor, not directly at the bank. He also discussed reported problems involving federal agencies, including the FAA and NSA, and the risks of trying to add new technology to legacy infrastructure.
Elliott compared the issue to moving water through pipes: high-capacity lines can carry a large flow until it reaches a narrower, outdated section. In technology, newer systems may run into limits imposed by old equipment and infrastructure.
“Unfortunately, they weren’t aware that they were going to create problems with that older technology,” Elliott said.
He said public officials may prioritize visible needs, such as repairing potholes, over less visible investments in digital infrastructure. That can leave organizations depending on systems that appear to function but have underlying weaknesses.
Elliott also warned that heavy reliance on a single technology provider can create widespread disruption. He cited a recent Office 365 outage that he said affected governments and businesses around the world.
Policymakers need a stronger grasp of technology, Elliott said, because they are responsible for decisions that affect public systems and data. Many elected officials, he argued, come from backgrounds such as law, business or the military, and may have little experience with technology.
Artificial intelligence can help identify software vulnerabilities, but applying fixes without careful testing can create new problems, Elliott said. An AI tool may flag a bug without understanding how a change could affect other systems or older infrastructure.
“You still have to take your time and go about it in a very measured way,” he said. “You need to test.”
Elliott likened the risk to repairing “old cloth with new thread.” A patch intended to fix one weakness could cause damage if it does not account for the system around it, he said.
For individuals, Elliott urged people to take an active role in protecting their personal information instead of assuming banks or retailers have every risk covered. Companies often use third-party vendors, he said, and consumers may not know which providers handle their data.
He recommended using two-factor authentication, changing passwords regularly and making a plan for what to do if personal information is exposed.
“Don’t just assume that the bank’s got it all covered,” Elliott said. “Don’t just assume that Amazon … has got all the security in place to protect you.”
Businesses should ask how they would respond to an attack and conduct tabletop exercises to practice their plans, he said. Government agencies should also prepare backups so they can continue delivering essential services during a cyber incident.
Elliott said hackers had tried to access Indiana’s critical 911 infrastructure, though the attempts had been unsuccessful at the time of the interview. He said backup systems had helped protect services in other situations.
Elliott described AI as a set of algorithms, not a thinking creature, but said it can be powerful in the hands of both malicious actors and cybersecurity professionals. Defending against attacks requires capable teams, careful implementation and ongoing attention to basic security practices.
“I want to say we, the American people, we are the target,” Elliott said. “So we’ve got to make sure we are protecting ourselves individually.”

